SOC Control Plane
Supercharge your SOC.
Bring threats, findings, quality, telemetry gaps, and detection coverage into one risk-scored Backlog, so analysts, engineers, and managers know what matters and what to do next. Meanwhile, retain a live risk view at all times.
Sound familiar?
Detection debt is burning out your teams
0 of 10. we solve all of them.
See how CraftedSignal helps →Answer does it affect us
Start lightweight: import assets, paste a plain description, or add services manually. CraftedSignal uses that business surface with threats, findings and telemetry to show what is relevant.
Learn more →One Backlog, risk-scored
New detections, false-positive tuning, missing telemetry, broken rules, mappings, tests and approvals land in the same queue. Meta-work inherits priority from what it unblocks.
Learn more →Fix safely, then prove it
Operators get direct actions: tune, map, test, enable telemetry, adopt a rule, hunt, accept residual risk or roll back. Impact preview and approvals keep production controlled.
Learn more →Write Sigma, deploy everywhere
Author in Sigma and convert to Splunk, Sentinel, CrowdStrike and Rapid7. Import native rules and translate to Sigma for portability, or keep writing in your SIEM's own language.
Learn more →Deploy safely, rollback instantly
Monitoring mode measures projected volume before alerting. Noise budgets block runaway rules. One-click rollback when things go wrong.
Learn more →Detections as Code
YAML rules in Git. Validate, test, and deploy with csctl or your CI/CD pipeline. Version history, diffs, and audit trail built in.
Learn more →Hunt, verdict, promote
Launch hypothesis-driven hunts against live SIEMs. Cluster results, verdict them in batch, and promote winning queries to tested Sigma rules in one click.
Learn more →Test live on your SIEM
Generate positive and negative test cases, push them to your SIEM, and prove the rule fires (or doesn't) on real data before a single alert reaches the analyst.
Learn more →Runbooks that stay in sync
Attach runbooks and playbooks to detections and hunts. Draft, review and refresh them from the same rule, test, threat and business details operators already inspect.
Learn more →Generation you can control
Self-host Ollama or point at any OpenAI-compatible endpoint. Disable generation entirely if policy requires it. Every suggestion is logged, reviewable, and non-destructive by default.
Learn more →Rank threats by relevance
Receive signed threat briefs with Sigma rules, IOCs and ATT&CK mapping. Each brief asks: does this affect us, can we see it and are we covered?
Learn more →Catch drift before auditors do
Every deployed rule is re-hashed on a schedule. Any out-of-band change in the SIEM gets flagged, diffed, and queued for review. Separation of duties, proven automatically.
Learn more →Analysts close the loop
SOC analysts verdict alerts TP / FP / noise in the same UI. Feedback becomes concrete Backlog work: tune this rule, retire that one, hunt this gap, ranked by impact.
Learn more →Noise budgets, enforced
Set a daily alert budget per team, per service, or per rule. Deploys that would blow the budget get held for review. Monitoring mode runs new rules silently until the volume proves out.
Learn more →Git-native backups
Every rule, every version, every test, pushed to your Git repo on a schedule. Restore from any point in history, audit offline, or migrate environments without touching the SIEM.
Learn more →SaaS, self-hosted, or air-gapped
Use SaaS, self-hosted, or air-gapped deployment. Regulated teams keep operational control, and MSSPs or enterprise teams can run with their own branding.
Learn more →How it works
From threat to risk-reducing work
Most detection tools start with a rule. CraftedSignal starts with the question that matters: does this affect us, can we see it, and are we covered?
Connect and import
Plug into Splunk, Sentinel, CrowdStrike and Rapid7, then import the rules you already run. Outbound-only agents query existing tools without moving raw logs into CraftedSignal.
Add business surface
Give as much or as little context as you have: manual services, regular imports, a free-text asset description today; CMDB, scanners and mapping later.
Triage threats and findings
Threat briefs, critical CVEs, pentest findings and future CTEM inputs are scored against the business surface, telemetry and current rule coverage.
Work one Backlog
Analysts and engineers see one risk-scored queue for rules, tuning, hunts, missing log sources, broken tests, mappings, approvals and residual-risk decisions.
Verify in your environment
Run tests and hunts against live SIEMs, check source mappings, preview alert volume and keep response steps with the rule before anything promotes.
Watch runtime risk
Risk scores change as threats move, assets change, rules break, false positives rise or telemetry disappears. Dashboards show what to know and what to focus on.
Some visual examples
See the platform in action
Every screen below is real product. No mockups, no composited dashboards. This is what a SOC team uses to see risk, coverage and work on a Monday morning.
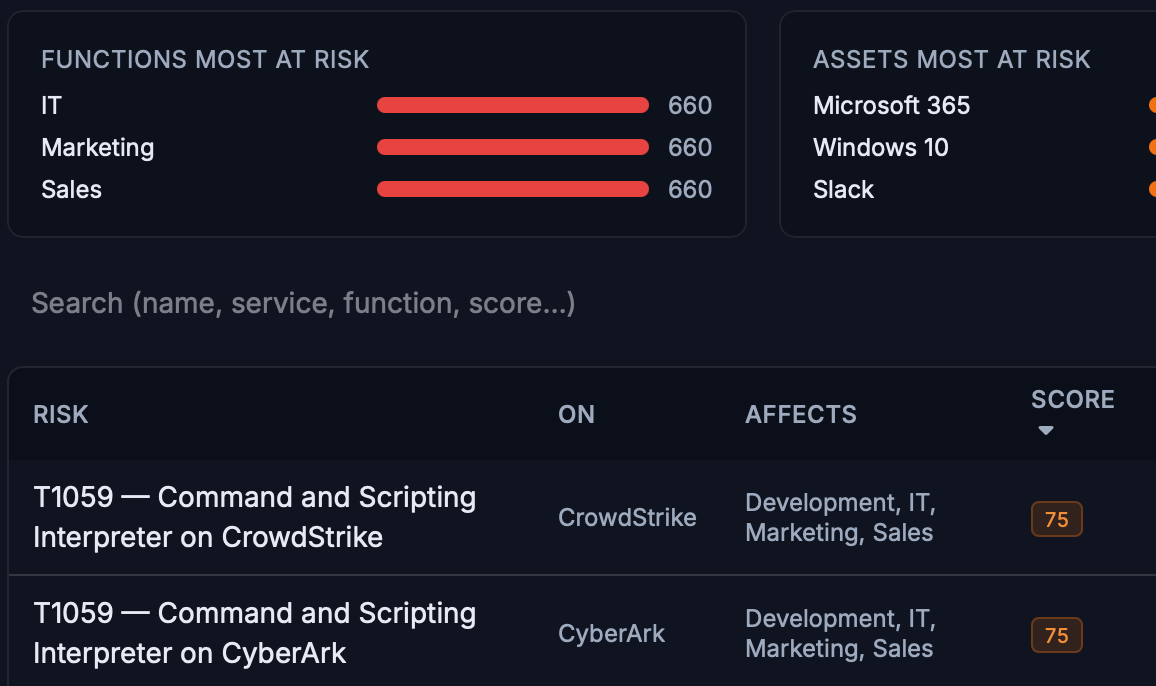
01 · Risk
One screen answers "are we covered?"
Exposure %, silently broken rules, SIEM health, and the top uncovered techniques with one-click Hunt / Rules actions.
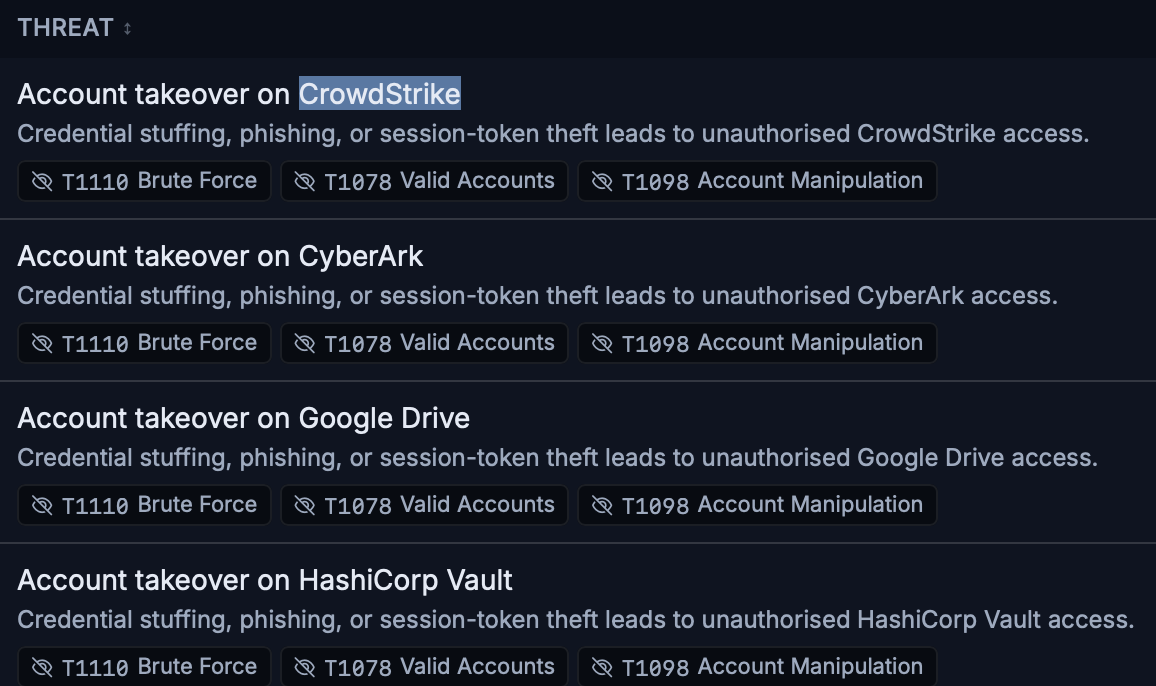
02 · Threat
Coverage depth, not just presence
Per-technique × per-layer heatmap (endpoint / network / identity / cloud / email). See where defense-in-depth is real and where it is paper-thin.
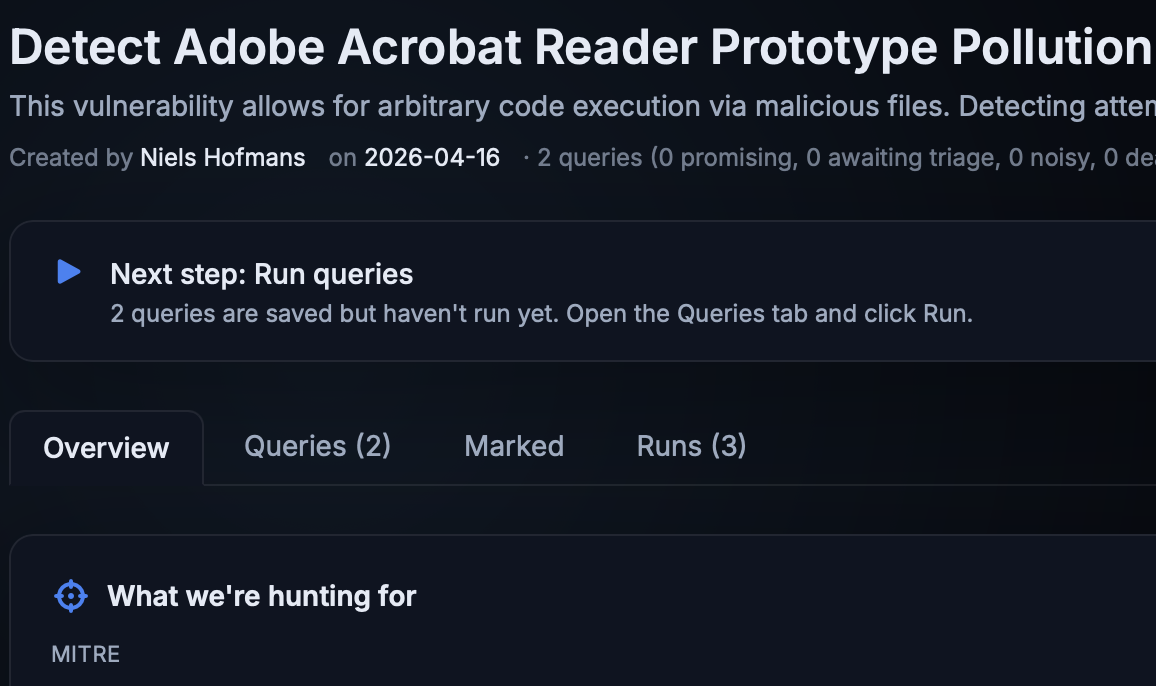
03 · Hunt
Cluster, verdict, promote
Hits grouped into clusters. One verdict covers dozens of rows. A promising query lands as a tested Sigma rule in a single click.
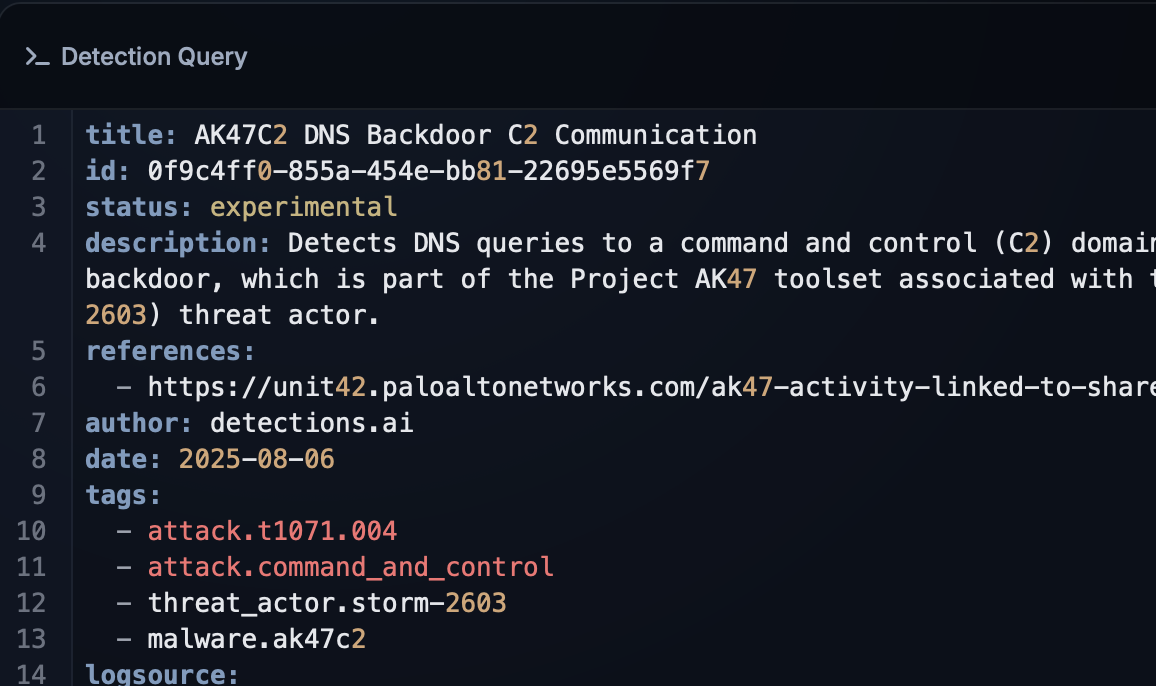
04 · Test
Write Sigma to every SIEM at once
The rule editor compiles on every keystroke. Splunk SPL, Sentinel KQL, CrowdStrike FQL, Rapid7 LEQL — all visible side-by-side with unmapped-field warnings.
04 · Test
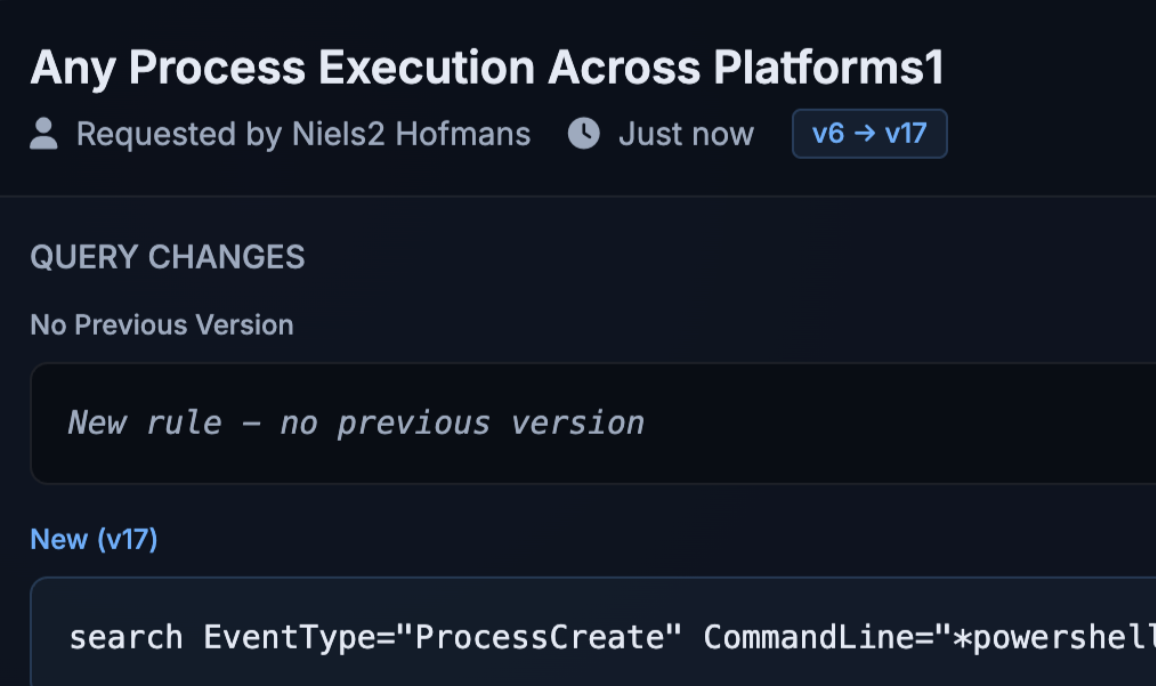
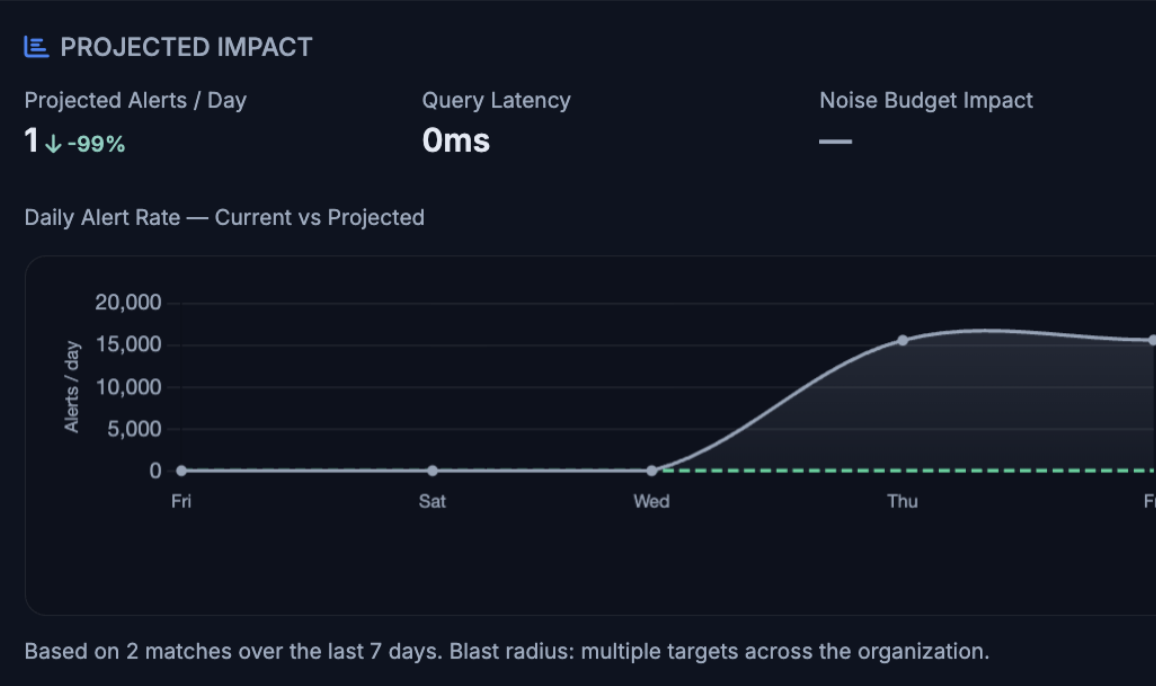
Approve with full context
Before/after query diff. Projected alert volume. Critical-severity policy reminders. Comments are mandatory on rejection.
05 · Monitor
Catch the rules that stopped firing
A dedicated queue for rules deployed and active but producing zero triggers. Grouped by owning team so the right person hears about it first.
Security evidence
Built for teams that need control and proof
Assistive generation, governed
Generated rules, tests, runbooks and playbooks stay reviewable and non-destructive. Nothing auto-deploys. Disable generation entirely if policy requires it.
Security controls included
SSO, Passkey MFA, audit logs, RBAC, approval workflows and exportable evidence. Every detection change is reviewable.
SaaS, self-hosted, air-gapped
Use SaaS, self-hosted, or air-gapped deployment. Keep operational control without moving raw logs into CraftedSignal.
Hardened cloud runtime
Private GKE, private Cloud SQL, KMS/CMEK, brokered application keys, Binary Authorization attestations and sovereignty-ready deployment options.
Ready to work the risks that matter?
I write rules
Start free. SaaS or self-hosted.
Start free →I manage a SOC
See how the Backlog reduces workload and improves coverage.
See ROI →I need governance
Audit logs, approvals, impact preview. Batteries included.
Learn more →Or talk to us: hello@craftedsignal.io